Bug Report:The logon is not encrypted/No login authentication #666

Open
opened 2026-10-05 00:10:19 +02:00 by adam · 4 comments
Owner

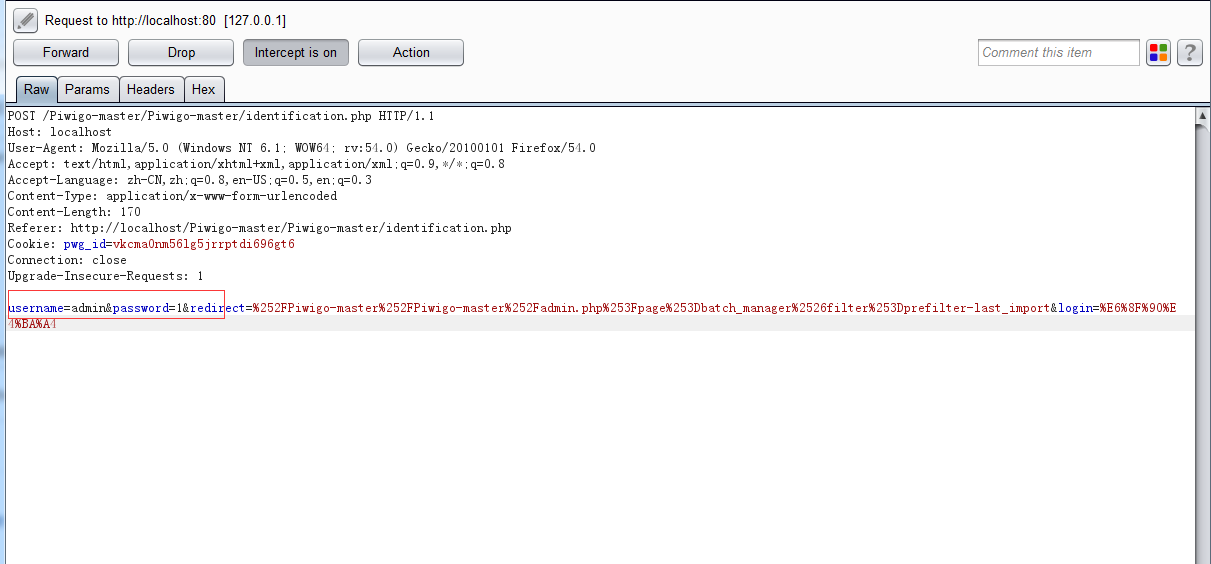
1.Packet at the login, no encryption
g dimbi8kd3cgvim y r4t

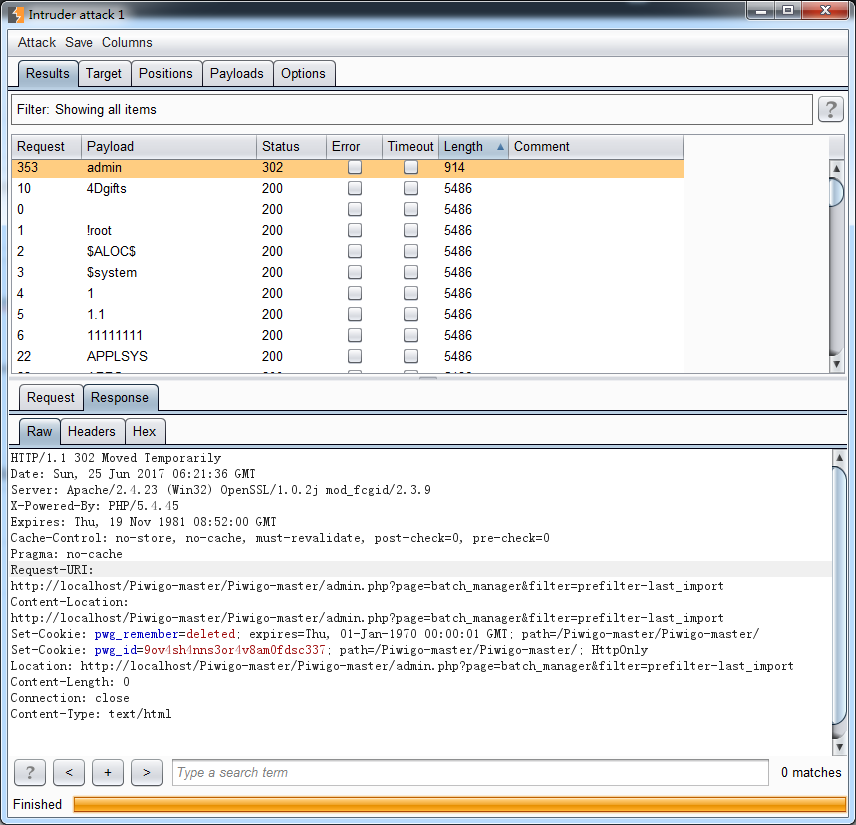
2.There were no restrictions on user input during the test
image

Evironment:
Windows XP Professional
Apache
MySQL
PHP 5.4.45
discovered by: mstteam(Linkey)

1.Packet at the login, no encryption ![g dimbi8kd3cgvim y r4t](https://user-images.githubusercontent.com/25584879/27514117-4501f9a6-59b3-11e7-835d-f512d5d40ab7.png) 2.There were no restrictions on user input during the test ![image](https://user-images.githubusercontent.com/25584879/27514134-10ae85e2-59b4-11e7-87b7-35049e7a67ec.png) Evironment: Windows XP Professional Apache MySQL PHP 5.4.45 discovered by: mstteam(Linkey) <!-- github-sync-id:238363740 -->
Author
Owner

The encryption is made at HTTPS level, if you have it. What other type of encryption are you expecting here?

The encryption is made at HTTPS level, if you have it. What other type of encryption are you expecting here? <!-- github-comment-id:311003917 -->
Author
Owner

@base64linqi see more --> stackoverflow

@base64linqi see more --> [stackoverflow](https://stackoverflow.com/questions/2336678/login-without-https-how-to-secure) <!-- github-comment-id:313596323 -->
Author
Owner

well the whole post on stackoverflow is to point out that there is no viable solution so...

well the whole post on stackoverflow is to point out that there is no viable solution so... <!-- github-comment-id:313643045 -->
Author
Owner

just a passerby here You're inspecting a http request over localhost, so it wouldn't be encrypted. Had you say had some type of self-signed cert and accessed https://localhost it would've shown encrypted. It's usually counter productive (key word usually, I'm sure there are some few special reasons for it) to do encryption over HTTP.

~~just a passerby here~~ You're inspecting a http request over localhost, so it wouldn't be encrypted. Had you say had some type of self-signed cert and accessed https://localhost it would've shown encrypted. It's usually counter productive (key word usually, I'm sure there are some few special reasons for it) to do encryption over HTTP. <!-- github-comment-id:315512844 -->
Sign in to join this conversation.
No labels
1 Participants
Notifications
Due Date
No due date set.
Dependencies

No dependencies set.

Reference: adam/Piwigo#666